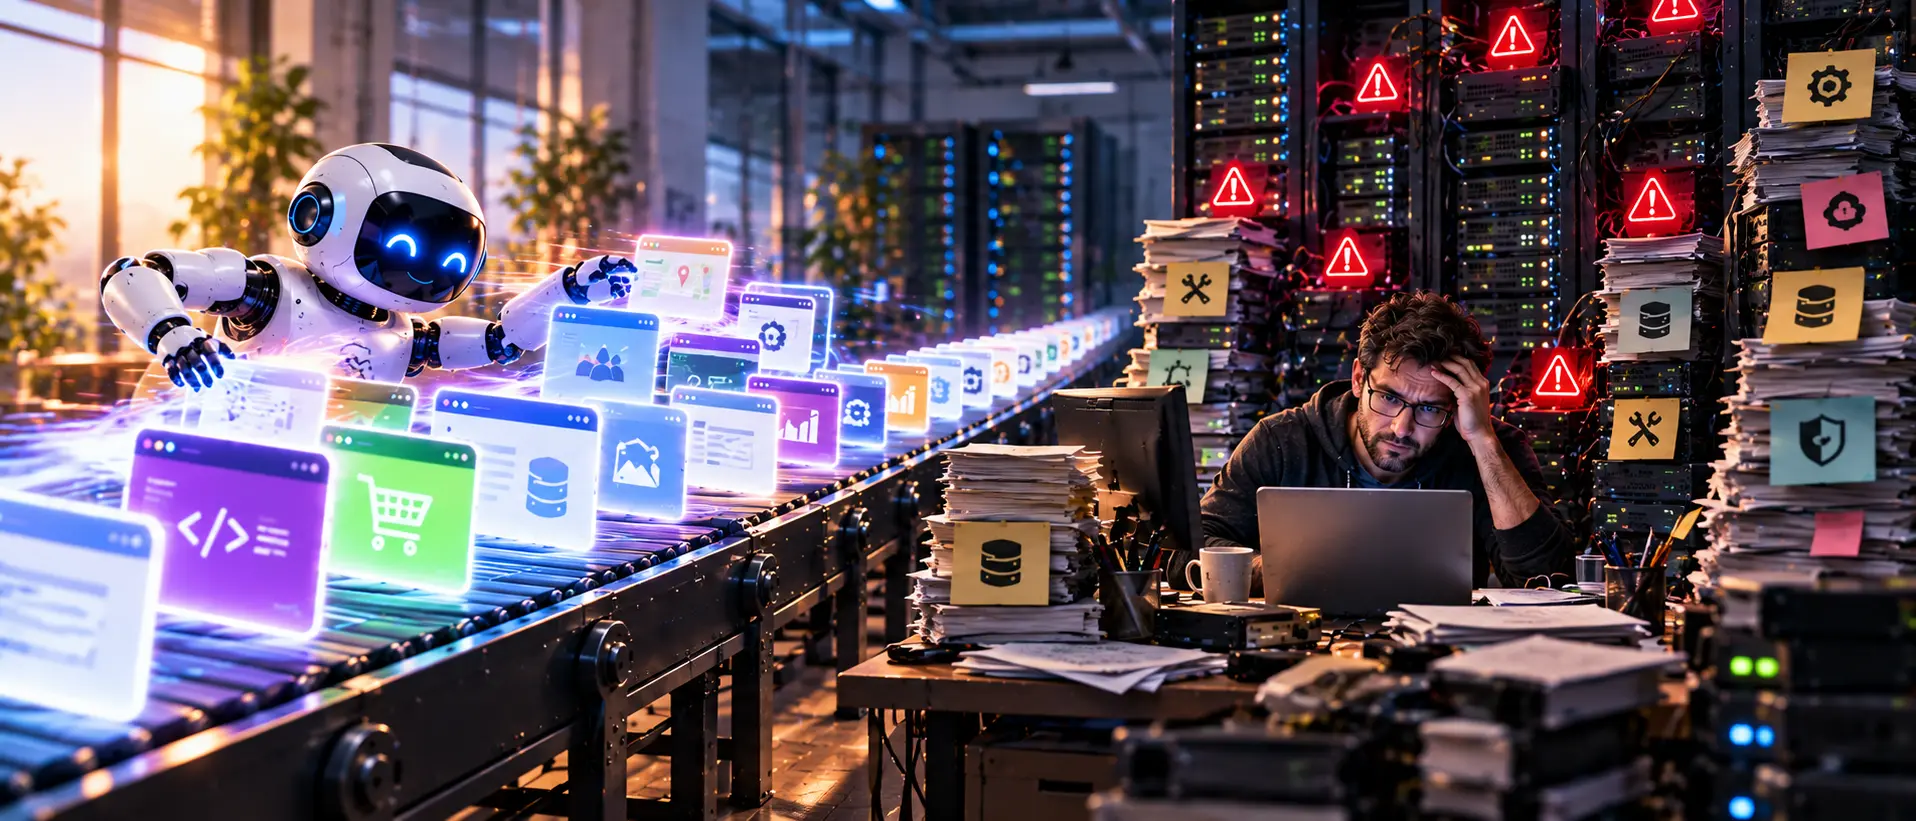
Software has never been easier to create, and we've never been better at finding its flaws. But as development becomes faster and cheaper, the responsibility for keeping everything running is becoming a much bigger job.
In May 2026, we published Dawn of the Software Singularity, exploring how artificial intelligence is fundamentally changing software development.
The premise was simple. Software that once required months or years of development, specialized knowledge, and substantial financial investment can increasingly be created in days, sometimes hours. AI is removing barriers that have long defined the software industry for decades.
AI can analyze entire codebases, explain how they work, and help anyone with sufficient technical understanding modify or expand them. Software is no longer dependent on the specialized knowledge of the person who originally wrote it. What once took a full-time software developer to accomplish might now occupy a fraction of their week.
But something interesting is happening on the other side of this equation.
The software still needs somewhere to run. It still needs to be maintained. It still needs updates, monitoring, backups, and more security than ever. And while the time required to create software is shrinking, the amount of software requiring that maintenance is growing just as fast.
PHP2Shell: A Glimpse of the New Reality
On October 21, 2026, the PHP project released a series of emergency security updates addressing two major critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, each rated 9.2 out of 10 for severity.
PHP is one of the most widely used programming languages on the web, powering everything from small business websites to major platforms like WordPress. Collectively dubbed PHP2Shell, these vulnerabilities could allow attackers to execute malicious code on any affected servers without so much as even a password, potentially gaining control of the systems hosting those websites.
The impact was immediate. Government websites across Europe, including services in France, the Netherlands, and Finland, were temporarily taken offline as administrators scrambled to protect their infrastructure. Wikipedia and the Internet Archive were also among the major services reported as affected by precautionary shutdowns. Meanwhile, technology giants including Microsoft, Amazon, and Cloudflare mobilized security responses to protect their customers.
Within days, security researchers had confirmed successful attacks.
For developers, the story demonstrated the growing capabilities of AI-assisted security research as these critical vulnerabilities were discovered with AI assistance by two research teams working independently, but for system administrators, it meant something very different.
Every affected environment needed immediate attention. Administrators had to identify vulnerable installations, evaluate exposure, obtain appropriate updates, consider compatibility with existing applications, deploy fixes, and verify that production services continued functioning.
In some environments, updating PHP is relatively straightforward. In others, applications depend on older versions, custom extensions, or configurations that make upgrading considerably more complicated. Who remembers what version of PHP Brian's old forgotten machine sat untouched since 2017 is running? Does anyone even still remember it exists?
And the work doesn't end when an update finishes installing. Administrators may also need to examine logs, investigate suspicious activity, and determine whether a system was compromised before it could be patched.
Multiply that across hundreds or thousands of servers and hundreds of thousands of websites, and the scale of the problem becomes apparent.
This is what modern system administration increasingly looks like.
We're Finding Problems Faster Than We Can Fix Them
Perhaps the most remarkable development isn't the increasing amount of software being written.
It's how quickly we're discovering problems in software that already existed.
For decades, vulnerabilities remained hidden inside applications, operating systems, libraries, and network services. Some existed for years before anyone recognized them.
Those problems were already there. We simply hadn't found them.
AI is changing that, and it's one of the most promising developments in cybersecurity.
Security researchers can now analyze enormous codebases, examine unfamiliar software, trace complicated dependencies, and uncover weaknesses at speeds that were previously unimaginable. Tasks that once required teams of specialists can increasingly be tackled by individuals with the help of AI. A developer trying to solve an unrelated problem might stumble upon a security flaw with AI's assistance, while experienced researchers can investigate far more software than ever before.
The result is a surge in vulnerability disclosures. Many of these flaws have been hiding in plain sight for years, and AI is finally helping bring them to light. PHP2Shell, for example, originated from code written by human developers over 14 years ago, long before modern AI coding tools existed. For more than a decade, the vulnerability remained undetected in one of the world's most widely used programming languages. AI helped uncover a problem humans had unknowingly introduced and overlooked for years, giving maintainers the opportunity to fix it.
Google's Threat Intelligence Group reported that monthly vulnerability disclosures more than doubled during 2026, rising from 5,045 in January to 10,740 in August.
The Forum of Incident Response and Security Teams (FIRST) also identified AI-assisted discovery, expanded reporting, and more aggressive security research as important contributors to the increase.
The growing volume of vulnerability reports is becoming difficult to ignore. Security researcher @callebtc captured the mood with a simple post.
I'm tired boss https://t.co/ix4S1OPmc2
— calle (@callebtc) October 22, 2026
"I'm tired boss," alongside a chart showing the dramatic rise in published CVEs (Common Vulnerabilities and Exposures). The chart illustrates the scale of the challenge facing security teams: as our ability to discover vulnerabilities accelerates, so does the work required to investigate, prioritize, and address them.
Finding vulnerabilities is a good thing, regardless of whether AI was involved or not. Every weakness discovered and responsibly disclosed is an opportunity to make software safer.
But discovery is only the beginning.
Someone must reproduce the issue, determine its severity, develop a correction, test the fix, coordinate its release, and distribute that updated software.
Then many more have to deploy it in the field. It's a massive undertaking for even small issues.
Finding a vulnerability may take minutes. Safely correcting it across many thousands of production systems may take days, weeks, or longer.
AI can assist with remediation too, but changes to production infrastructure still require validation. A technically correct patch can break an application, disrupt a dependency, or create an unexpected operational problem.
We are entering an era where vulnerabilities can be discovered at machine speed, while much of the responsibility for fixing them still operates at human speed.
And as more researchers begin using AI, the volume of discoveries may continue growing.
The challenge isn't simply patching everything as quickly as possible. Not every reported vulnerability is exploitable in every environment, and not every disclosure deserves the same urgency. Administrators must increasingly distinguish immediate threats from theoretical risks while keeping essential services available.
The More We Build, the More We Have to Maintain
Our original software singularity argument focused on what happens when the cost of creating software approaches zero.
Historically, development costs acted as a natural limitation. Businesses had to justify the expense of building a new application. Developers had limited time. Small organizations often relied on existing products because custom software was too expensive, but now AI has removed many of these constraints.
Need a custom reporting dashboard? Do it.
Need an application to automate a repetitive task? Build one.
Need an integration between two systems that weren't designed to communicate? No problem.
These are genuinely useful capabilities, and they allow smaller organizations to accomplish things that were previously only practical for companies with substantial development budgets.
But each new application introduces another set of operational responsibilities. It may require any number of databases, web servers, authentication systems, external APIs, third-party libraries, scheduled tasks, monitoring, backups, and many ongoing updates.
Every dependency is another component that may eventually require maintenance. An application that takes only an afternoon to create can suddenly become something an organization depends on for years.
And unlike development time, operational responsibility accumulates. The first application needs maintenance. So does the second. And the third. And the hundredth. Software development is becoming cheaper, but operating software has not become free.
The Changing Economics of Technical Work
Consider a small company ten years ago.
It might have employed a full-time developer to build and maintain internal applications, while relying on a part time system administrator for occasional server maintenance, updates, and troubleshooting.
The developer spent most of their time writing code, implementing features, and understanding systems that few other people could modify.
The administrator kept the infrastructure running, applying updates and responding when something broke.
Now consider that same company using modern AI development tools.
A developer may be able to accomplish in days what previously required weeks. Another employee may be able to modify an existing application without needing to understand every detail of its original implementation.
Even the knowledge of the person who wrote the software is becoming less of a barrier. AI can examine a codebase, explain its architecture, identify dependencies, and help a new developer continue where the original author left off.
The amount of developer time required to maintain a given application has shrunk dramatically.
Meanwhile, the company may now operate several times as many applications, each with its own dependencies, security considerations, and operational requirements.
The workload has shifted.
What previously justified a full-time development position may now require a part time role, while the infrastructure that once received occasional attention may now require dedicated, ongoing support.
This won't happen uniformly across every organization, complex software engineering still presents difficult problems, and AI doesn't eliminate the need for experienced developers, but for many businesses, particularly those operating ordinary web applications and internal tools, the balance of technical labour is changing drastically.
System Administration Has Become a Security Profession
There was a time when system administration at a small company could largely consist of provisioning servers, managing accounts, applying occasional updates, monitoring available resources, and responding to failures.
Those responsibilities still exist.
But today's administrator must also contend with a rapidly changing security environment.
A typical server runs an operating system, web server, application runtime, database engine, monitoring agents, backup software, management interfaces, and numerous supporting libraries. Each component has its own update schedule, vulnerabilities, configuration requirements, and dependencies. A vulnerability discovered in a single widely used library can suddenly put thousands of otherwise unrelated applications at risk, leaving administrators responsible for identifying which systems are affected and how urgently they need attention.
Managing this environment requires a detailed understanding of how everything fits together. Administrators need to know which software is installed, how it's exposed to the internet, what resources it can access, and which other systems depend on it. They must also maintain reliable backups, control access, monitor logs, test recovery procedures, and ensure that security updates don't inadvertently break critical services. Much of this work happens behind the scenes, often going unnoticed until something goes wrong.
When a serious vulnerability becomes public, those responsibilities become considerably more urgent. Administrators may have only hours to assess their exposure, determine whether a patch is available, evaluate the consequences of applying it, and decide whether vulnerable services need to be restricted or temporarily shut down. Every decision involves balancing security against the availability of systems that businesses and customers depend on.
PHP2Shell demonstrated just how far these responsibilities extend. The vulnerabilities existed within PHP itself, meaning a developer could have written perfectly reasonable, secure application code and still been exposed through the underlying runtime. Protecting affected systems required action from hosting providers, infrastructure operators, security teams, and administrators, regardless of who originally developed the applications.
As software becomes more widespread and interconnected, system administration increasingly encompasses cybersecurity, incident response, risk management, and business continuity. The technical knowledge required is growing alongside the consequences of getting something wrong, making experienced administrators an increasingly important part of keeping modern infrastructure secure and operational.
AI Can Help Administrators Too
There is an obvious question here.
If AI can dramatically reduce software development time, why can't it do the same for system administration? And to a considerable extent, it can.
AI can help analyze logs, identify vulnerable software, generate configuration changes, write automation scripts, investigate incidents, and explain unfamiliar infrastructure. All tasks that once required extensive manual research can now be completed much faster. The same tools transforming software development are already transforming infrastructure management.
But production systems introduce a different set of constraints.
Generating a configuration is relatively easy. Knowing whether applying it will interrupt hundreds of customers is considerably harder. An AI can suggest a database upgrade. Someone still needs to understand whether the application supports it, whether the backup is recoverable, and what happens if the upgrade fails.
An AI can write a script to modify firewall rules, but someone must still ensure that the changes won't disconnect critical systems or expose services that should remain private.
And while increasingly autonomous tools may eventually handle more of these responsibilities, they introduce their own questions about permissions, verification, accountability, and failure recovery.
The Real Cost of Software Is Changing
For decades, organizations often treated software development as the primary expense.
Building the application required significant investment. Once completed, keeping it running was sometimes considered a comparatively minor ongoing cost.
However, if an application can be built in a few days, but requires years of hosting, monitoring, security updates, maintenance, and incident response, its operational lifetime may represent a much larger portion of its total cost than the original development.
Who will maintain it? Who will monitor it? Who will respond when one of its dependencies becomes vulnerable? Who will recover it when something fails?
The software singularity represents an extraordinary expansion of what individuals and small organizations can accomplish. We're gaining the ability to create tools that would have been financially or technically impractical only a few months ago. At the same time, we're gaining the ability to examine existing software with unprecedented speed and discover weaknesses that might otherwise have remained secretly exploited for decades.
Both developments are positive.
More accessible software development creates opportunities. Better vulnerability discovery makes it possible to address longstanding security problems. However, together, they create an enormous operational challenge.
The traditional developer who once spent months writing an application may now complete that work in days.
The system administrator who once spent a few hours each week maintaining the resulting infrastructure may now face a continuous cycle of updates, vulnerability assessments, security incidents, and operational decisions.
The balance of technical work is changing, and organizations will need to change with it.
The software singularity is making the creation of software increasingly accessible to everyone, but every application still needs somewhere to live.
We've made building software easier than ever before.
Now we have to figure out how to maintain it all.